What are UK GDPR and PECR rules for B2B email?
Also called: PECR, UK GDPR, GDPR B2B email
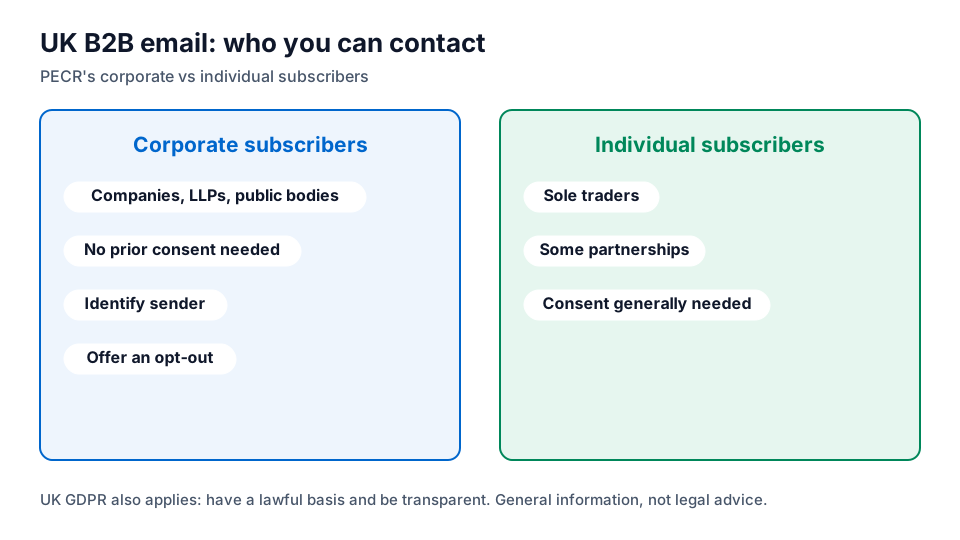
In the UK, B2B email marketing is governed by PECR, which sets the rules for electronic marketing, and by UK GDPR, which governs the personal data involved. Emails to corporate addresses don't need prior consent under PECR but must identify the sender and offer an opt-out; individual and sole-trader addresses generally need consent.
Why it matters for healthcare sales and marketing
Teams reaching UK healthcare organizations need to know which contacts can be emailed and on what basis. The rules differ from both the U.S. and Canada.
How it works
- PECR, corporate subscribers: companies, LLPs and public bodies can receive B2B marketing email without prior consent, with sender identification and an opt-out.
- PECR, individual subscribers: sole traders and some partnerships are treated like individuals and generally need consent.
- UK GDPR: a named person's work email is personal data, so you need a lawful basis (often legitimate interests), transparency about how you got the data, and respect for objections.
Example
Illustrative scenario. A health IT company emails named IT leaders at NHS trusts and private hospital groups on a legitimate interests basis, with a clear privacy notice and opt-out, and keeps sole-practitioner contacts out of email campaigns unless they have consented.
Common mistakes
- Treating all UK contacts the same. Corporate and individual subscribers differ.
- No privacy information. Tell people how you got their data.
- Applying UK rules across the EU. EU countries have their own laws.
Related terms
Put it to work
- Compliance questions in our FAQ: short answers on email rules
- International healthcare data: reaching professionals outside the U.S.
- Security and compliance: our compliance guidelines
Sources
- Guide to PECR: electronic mail marketing, Information Commissioner's Office
- Legitimate interests, Information Commissioner's Office